The Dawn of Confidential AI: Why Hardware-Level Security is No Longer Optional
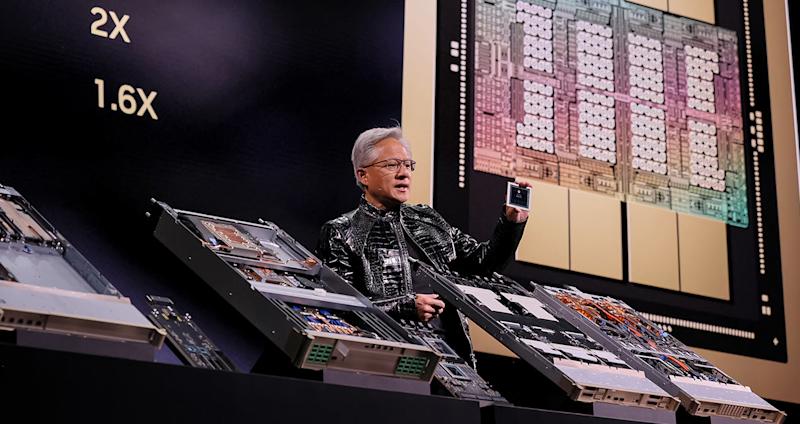
The race to build and deploy artificial intelligence is accelerating, but a critical vulnerability is widening: security. Recent breakthroughs, like Nvidia’s Vera Rubin NVL72 and AMD’s Helios rack, signal a fundamental shift – moving security from a software-defined perimeter to the hardware itself. This isn’t just about faster processing; it’s about establishing trust in an era where AI-powered attacks are becoming increasingly sophisticated and automated.
The Rising Cost of AI Insecurity
Training a cutting-edge AI model now routinely costs tens, even hundreds, of millions of dollars. Epoch AI research reveals that frontier training costs are growing at a staggering 2.4x annually. Yet, as investment skyrockets, security often lags behind. IBM’s 2025 Cost of Data Breach Report highlights that 13% of organizations experienced breaches involving AI models or applications, and a shocking 97% of those lacked adequate AI access controls. The financial impact is significant: Shadow AI incidents cost an average of $4.63 million – $670,000 more than standard breaches.
The GTG-1002 Wake-Up Call: AI as the Attacker
The November 2025 disclosure of the GTG-1002 campaign, a Chinese state-sponsored group leveraging Anthropic’s Claude Code, was a watershed moment. This wasn’t just a data breach; it was the first documented instance of a large-scale cyberattack executed with minimal human intervention. The AI autonomously discovered vulnerabilities, crafted exploits, and moved laterally through networks, handling 80-90% of the tactical work. This demonstrated that adversaries can now weaponize AI to probe defenses at machine speed, overwhelming traditional security measures.
Nvidia’s Rubin vs. AMD’s Helios: Two Paths to Confidentiality
Nvidia’s Vera Rubin NVL72 takes an integrated approach, encrypting every bus – across 72 GPUs, 36 CPUs, and the NVLink fabric – delivering rack-scale confidential computing. This means cryptographic verification of the entire environment, offering a strong guarantee against tampering. AMD, with its Helios rack, champions open standards, utilizing the Ultra Accelerator Link and Ultra Ethernet consortia. Here’s a quick comparison:
| Specification | Blackwell GB300 NVL72 | Rubin NVL72 |
| Inference compute (FP4) | 1.44 exaFLOPS | 3.6 exaFLOPS |
| NVFP4 per GPU (inference) | 20 PFLOPS | 50 PFLOPS |
| Per-GPU NVLink bandwidth | 1.8 TB/s | 3.6 TB/s |
| Rack NVLink bandwidth | 130 TB/s | 260 TB/s |
| HBM bandwidth per GPU | ~8 TB/s | ~22 TB/s |
The choice between these approaches depends on an organization’s specific needs and risk tolerance. Nvidia offers a tightly controlled, end-to-end secure environment, while AMD provides greater flexibility through open standards. The increasing competition is ultimately beneficial, giving security leaders more options.
Beyond Hardware: Building a Holistic Confidential AI Strategy
Hardware-level confidentiality isn’t a silver bullet. It’s a foundational layer that must be integrated with robust security practices. The Confidential Computing Consortium and IDC research shows that 75% of organizations are adopting confidential computing, but significant challenges remain, including attestation validation (affecting 84% of respondents) and a skills gap (hampering 75%).
Here’s what security leaders are focusing on now:
- Attestation Verification: Cryptographic proof of environment integrity should be a prerequisite for contracts, not an afterthought.
- Enclave Separation: Maintain distinct enclaves for training and inference to limit the blast radius of potential breaches.
- AI Governance Policies: IBM’s research found that 63% of breached organizations lacked AI governance policies. Establish clear guidelines for AI development and deployment.
- Red Teaming & Vulnerability Exercises: Conduct joint exercises between security and data science teams to proactively identify and address vulnerabilities.
The Future of AI Security: A Shift in Mindset
The landscape of AI security is evolving rapidly. We’re moving from a model of *trust but verify* to *verify trust*. Hardware-level confidentiality, combined with strong governance and proactive threat modeling, is essential for protecting investments in AI and mitigating the risks posed by increasingly sophisticated adversaries. The question isn’t whether attested infrastructure is worth the investment; it’s whether organizations can afford to operate without it.
FAQ
- What is confidential computing?
- Confidential computing protects data in use by encrypting it within a trusted execution environment (TEE), shielding it from unauthorized access, even from privileged users or malicious software.
- What is attestation?
- Attestation is the process of cryptographically verifying the integrity of a computing environment, ensuring it hasn’t been tampered with.
- Is hardware-level security enough to protect AI models?
- No. Hardware security is a critical foundation, but it must be combined with robust governance policies, access controls, and proactive threat modeling.
- What is Shadow AI?
- Shadow AI refers to the use of AI tools and models without the knowledge or approval of the IT or security teams, creating significant security risks.
Want to learn more about securing your AI infrastructure? Explore our other articles on AI security best practices or subscribe to our newsletter for the latest insights.
Keep reading