Refrigeration Unit Cyberattacks
European supermarkets face potential infrastructure failures following remote cyberattacks that disabled commercial refrigeration units across at least 12 countries in October and November, Seznam Zprávy reported.
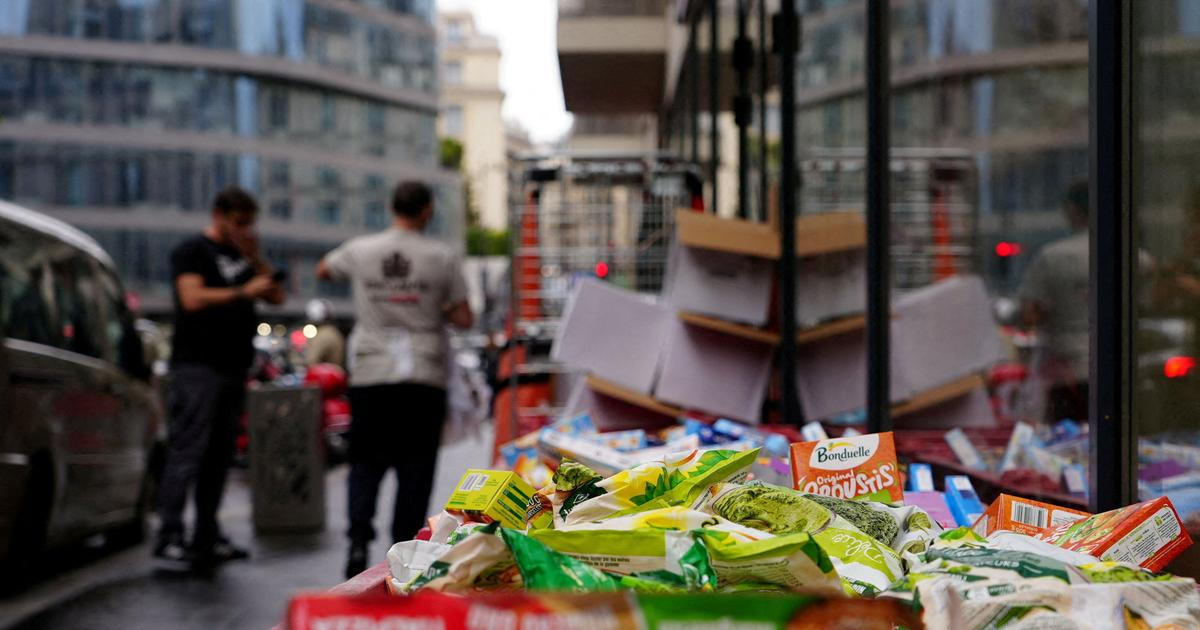
Hackers penetrated remote management controls and forced units into defrost cycles. This pushed internal temperatures as high as 50 degrees Celsius, spoiled tons of food, and caused physical fires in specific locations, according to reporting by Aktuálně.cz.
France formally attributed the operation to a cyber unit linked to the Iranian Revolutionary Guard Corps. French Foreign Minister Jean-Noël Barrot stated on Monday that the incidents represented a targeted sabotage campaign against French interests, pointing to the hacker collective Shahid Kaveh.
European Supermarket Vulnerabilities
The first wave of intrusions hit roughly 700 retail locations across France on the night of October 11. A second wave followed in early November, disrupting operations in Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal, and Sweden, according to AFP data.
Many targeted systems relied on default factory credentials or maintained continuous remote access connections required by third-party maintenance vendors. Forum 24 noted that researchers from Palo Alto Networks observed a drop in publicly accessible industrial refrigeration devices in France from over 1,850 down to 316 following the alerts.
French authorities also recorded an attempted intrusion targeting the cooling systems of the French Blood Transfusion Service. Monitoring systems detected and blocked that breach before any blood supplies or vaccine samples suffered damage, Health-ISAC reported.
Iranian State Attribution
Parisian prosecutors requested international arrest warrants for the commander of the Shahid Kaveh unit and two deputies. French authorities traced the digital fingerprints of the intrusion through IP addresses located inside Iran and the use of the Persian language in system logs, as detailed by Aktuálně.cz.
The Iranian Ministry of Foreign Affairs rejected the accusations as baseless and one-sided. In an official statement cited by AFP, Iranian diplomacy dismissed the claims by stating that a government failing to manage internal domestic cooling controls should not blame foreign actors.
Despite the official Iranian denial, foreign policy officials in Paris summoned the Iranian ambassador. Minister Barrot announced that France would coordinate with European Union partners on potential sanctions responses without imposing self-imposed restrictions.
Future Infrastructure Risks
Juhan Lepassaar, head of the European Union Agency for Cybersecurity (ENISA), warned on Tuesday that consumer routers, smart home appliances, and vital municipal networks remain exposed to identical remote tactics. He noted that security often takes a secondary priority until a major operational failure occurs.
ENISA emphasized that preventive cybersecurity measures require significant financial investment across both public and private sectors. Experts from the firm Wavestone told reporters that state-backed actors currently target simple connected hardware before potentially moving toward power distribution grids and water supply networks.
European Commission officials released a joint statement on November 4 urging immediate vulnerability patching across commercial refrigeration hardware. The advisory stresses that continuous vendor access protocols must be re-evaluated to prevent unauthorized remote tampering.
Questions About European Supermarket Refrigeration Failures
Which countries experienced supermarket refrigeration failures?
Commercial grocery stores suffered temperature spikes in at least 12 European nations, including France, Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal, and Sweden.
What specific hacking group was blamed for the sabotage?
French authorities identified the Shahid Kaveh hacking unit, which operates under the direction of the Iranian Revolutionary Guard Corps, as the primary perpetrator behind the operational disruption.
How did the hackers manipulate the cooling systems?
Intrusion operators exploited weak remote access controls and default manufacturer passwords to override industrial refrigeration units and manually activate high-temperature defrost cycles.
Are other connected devices at risk of similar attacks?
ENISA leadership warned that smart home appliances, network routers, and essential municipal infrastructure face comparable cyber vulnerabilities if foundational device security standards remain neglected.