
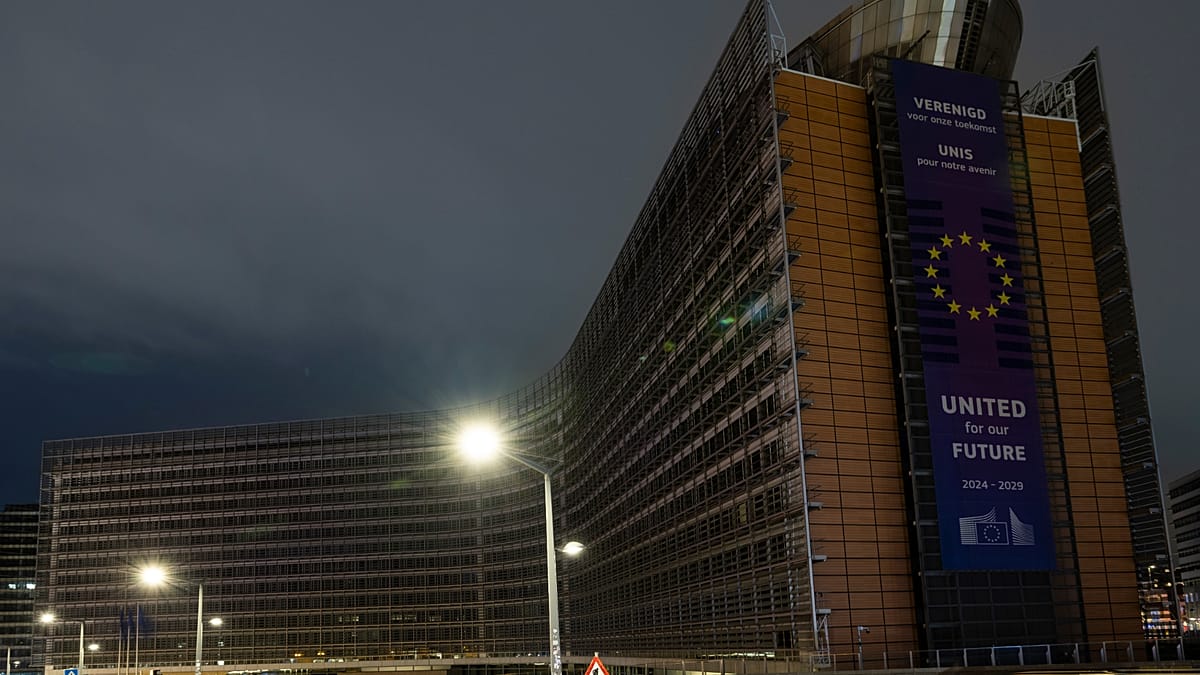
The European Commission confirmed on November 19 that it was hit by a cyberattack using artificial intelligence tools, first detected on October 22. euronews reported the Commission did not receive any ransom demand.
AI tool linked to vulnerability exploitation
Spokesperson Thomas Regnier told reporters the campaign relied on a publicly available AI tool named ARTEX, which identifies software vulnerabilities that can be patched or exploited. “This was an AI-generated cybercampaign,” Regnier said. He declined to attribute the intrusion to a specific actor or confirm whether it was still ongoing.
“I can confirm that the commission has recently taken necessary steps in response to a detected cybercampaign,” spokesperson Thomas Regnier said.
Commission took HR and medical systems offline
The Commission preventively took down several internal applications to stop the attack from spreading. Politico reported that systems including Sysper — the HR platform for payslips, time management and holidays — and the Joint Sickness Insurance Scheme (JSIS) for medical reimbursements were offline for around 10 days. By November 19, Sysper had been restored while JSIS remained unavailable, two EU officials told euronews.
No evidence of broad data breach, investigation continues
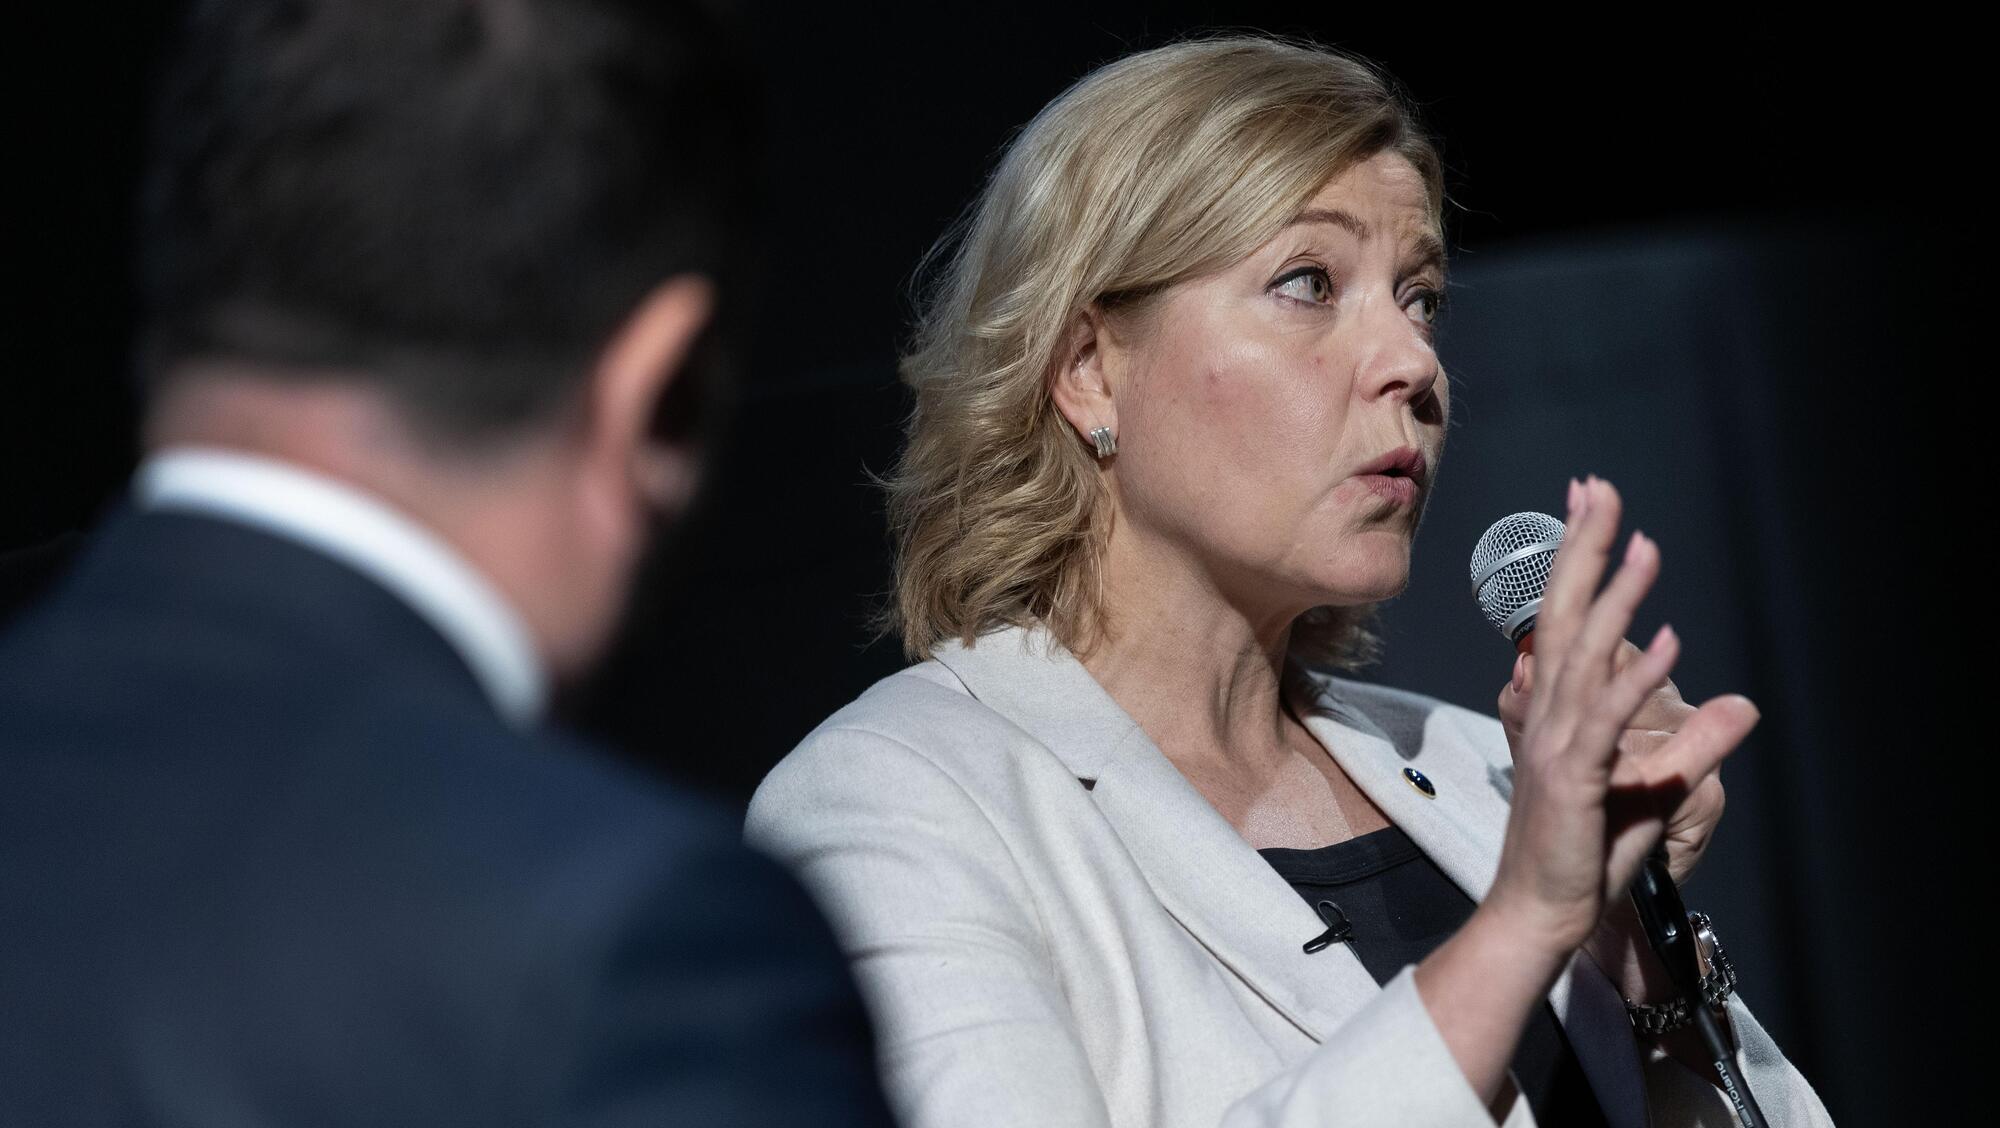
“We have not detected any evidence of a data breach affecting Commission staff as a whole,” Regnier said. The Commission convened its highest-level internal crisis management body for an urgent meeting, and Tech Sovereignty and Security Commissioner Henna Virkkunen briefed other commissioners on November 18, Politico reported. CERT-EU and the European Data Protection Supervisor have been informed.
Sensitive personal data at stake
The compromised platforms hold officials’ names, pay grades, home addresses and contact details. Such a database could fuel more sophisticated campaigns targeting individual staff, euronews noted. The Commission’s internal documents are hosted on a separate system. EU officials had not received official internal communications about the incident as of November 19, as the extent of damage is still being assessed.
Criticism over transparency
“The problem I have with the European Commission is that they keep the information about it internally and don’t disclose it to the public,” said Bart Groothuis, a Dutch MEP from the Renew group, speaking to euronews.
“Each time they don’t bring information to the public about intrusions that hit EU institutions, bodies and agencies, they miss an opportunity to explain and sell the economic security policy we set out as the EU against our adversaries.”
Pattern of recent intrusions
The Commission’s cloud infrastructure hosting Europa.eu websites was compromised in March, resulting in the theft of around 91.7 GB of data including personal information and email content, euronews reported. In January, a cyberattack targeted the Commission’s central mobile-device infrastructure, potentially exposing staff names and phone numbers.
Henna Virkkunen, who briefed commissioners on the intrusion on November 18, became Executive Vice-President of the European Commission for Technological Sovereignty, Security and Democracy and Commissioner for Digital and Frontier Technologies in December 2024.
A member of Finland’s National Coalition Party, she previously served as an MEP from 2014 to 2024 and held three ministerial posts in Finnish cabinets between 2007 and 2014, including Minister of Education and Minister of Transport and Local Government. In 2026, Time magazine named her the only Finn among the 100 most influential people in the world.
What remains unknown
The full extent of any damage remains unclear, Politico said citing an EU official. The identity of the attacker, whether sensitive staff data was stolen, and whether the campaign is still active are all unanswered as the investigation by DG DIGIT continues.
FAQ: European Commission AI cyberattack
When was the attack first detected? The intrusion was first detected on October 22, 2026, the Commission confirmed on November 19.
What AI tool was used? Spokesperson Thomas Regnier identified the tool as ARTEX, a publicly available application that identifies software vulnerabilities.
Was any data stolen? The Commission says it has not detected evidence of a data breach affecting staff as a whole, but the full extent of damage is still under investigation.
Which systems were affected? Sysper (HR, payslips, time management) and the Joint Sickness Insurance Scheme (medical reimbursements) were taken offline for about 10 days. Sysper was restored by November 19; JSIS remained down.
Has the attacker been identified? No. Regnier declined to attribute the campaign to a specific actor.
Was a ransom demanded? The Commission said it did not receive any ransomware request.
Worth a look