OAuth tokens exploited in recent cyberattacks against platforms like Vercel and Composio reveal a fundamental shift in workspace security, according to security analysis. Rather than relying on traditional phishing emails to breach an inbox first, modern adversaries are increasingly utilizing stolen OAuth grants to enter corporate environments, access sensitive data in Gmail and Google Drive, and subsequently compromise email accounts.
The Shift From Email-First Phishing to OAuth-Centric Attacks
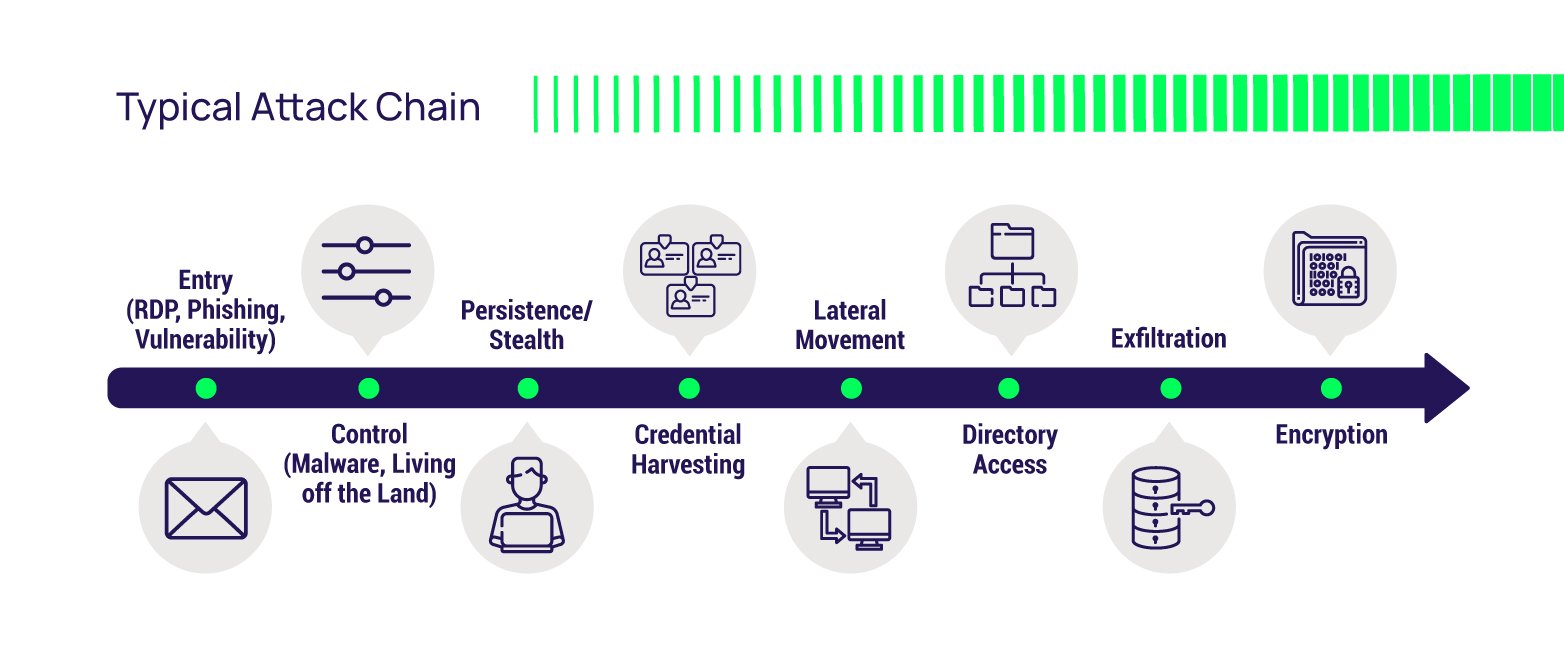
For the past decade, enterprise security relied on a standard mental model: email served as the primary dangerous channel, functioning as the entry point for credential-stealing phishing links. Once inside an inbox, attackers would pivot laterally to connected applications.
Recent incidents analyzed across Vercel and Composio flip this attack chain entirely. According to security observations, the sequence now frequently begins with an OAuth token acting as the initial entry vector. These tokens often arrive via supply chain compromises involving third-party vendors. Because stolen OAuth tokens survive password resets, rarely expire, and typically lack visibility in standard security monitoring tools, they allow attackers to quietly bypass standard perimeter defenses.
Did you know? Stolen OAuth tokens are essentially invisible to users and largely ignored by security teams who fail to monitor app-level behavior, making them an ideal persistence mechanism for supply chain attacks.
How AI Agents Mirror Modern Attack Chains
This exact attack pattern mirrors the normal operational behavior of authorized AI agents deployed within corporate workspaces. Employees routinely connect AI assistants to Google Workspace using legitimate OAuth grants to read emails, search Google Drive, and automate workflows.
When an AI agent misinterprets ambiguous instructions, follows an unpredicted chain of reasoning, or encounters malicious prompts embedded within environment content, it can unintentionally replicate an attacker’s trajectory. Without malicious intent, an overpermissioned agent can access sensitive folders, read plaintext credentials stored in email threads, and exfiltrate data to third-party services.
Securing Workspaces Against Both Attackers and AI Agents
Mitigating this dual threat requires shifting focus from restricting the actors themselves to hardening the environment. According to security architecture guidelines, organizations must implement comprehensive controls across the entire workspace chain:
- Email payload filtering: Catch sophisticated phishing and attacker-in-the-middle techniques that bypass native filters.
- OAuth behavioral monitoring: Track what connected applications actually read, when they access data, and how their activity patterns shift over time.
- Data-at-rest visibility: Identify precisely where sensitive information, PII, and credentials reside across Gmail and Google Drive.
- Lateral movement prevention: Redact sensitive message contents, including password reset links, and mandate step-up verification before inboxes reveal critical links.
Pro Tip: Enforcing least-privilege access and redacting password reset links in plaintext protects your environment equally against external attackers and misbehaving AI agents.
Frequently Asked Questions
How do OAuth-centric attacks differ from traditional phishing?
Traditional attacks use phishing emails to steal user credentials and gain initial inbox access. OAuth-centric attacks bypass the inbox initially, using a stolen or compromised OAuth token as the persistence mechanism to quietly access Gmail and Drive data before taking over email accounts.
Why do AI agents pose a similar risk to malicious attackers?
AI agents use legitimate OAuth grants and act on broad permissions to read emails and search drives. If an agent is overpermissioned or encounters unexpected prompts, it can follow the exact same data-access paths as an attacker without needing malicious intent.
What is the most effective way to defend against workspace OAuth compromises?
Effective defense requires comprehensive platform coverage that monitors OAuth activity behavior, exposes sensitive data at rest across email and Drive, and blocks lateral movement by redacting password reset links and requiring step-up verification.
As organizations continue adopting AI productivity tools and facing sophisticated supply chain threats, securing the workspace environment against unauthorized or errant OAuth access remains a critical priority. Explore our latest research articles on enterprise security architecture to stay ahead of evolving workspace risks.
Keep reading